 Русский
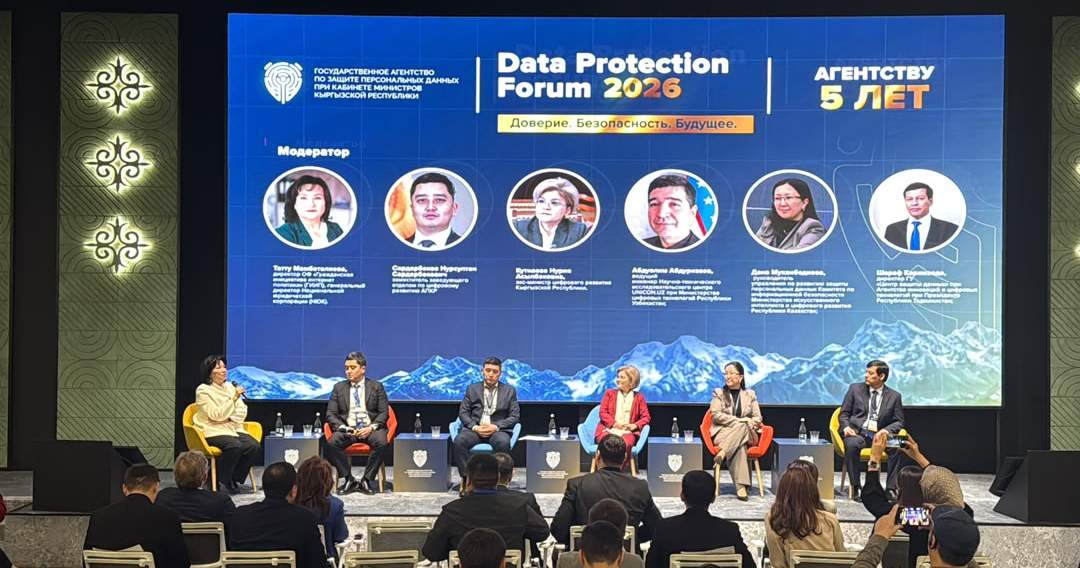
The Data Protection Forum 2026, themed “Trust, Security, and the Future,” was held at the IT-Hub Technopark in Bishkek. The event was organized by the State Agency for Personal Data Protection under the Cabinet of Ministers of the Kyrgyz Republic to mark its fifth anniversary. The Digital Sustainability Association also participated in the forum.
About the Forum
The forum brought together representatives from the government, the business sector, and the international expert community to discuss four key topics: personal data protection, cybersecurity, artificial intelligence, and the digital state. Speakers included the Agency’s Director, Kutman Mamyrov; the European Union Ambassador to the Kyrgyz Republic, Rémi Duflou; representatives from the e-Governance Academy, Deloitte, and Kaspersky (Kazakhstan); as well as colleagues from Kazakhstan, Tajikistan, and Azerbaijan. The forum was supported by partners including the European Union, the OSCE, Beeline, Expertise France, the ITU, and other organizations.
Program Highlights
- A review of the Agency’s five years of work, covering legislative development, institutional establishment, and law enforcement.
- The launch of a new “Personal Data Usage Monitoring” service within the “Tunduk” mobile app, which allows citizens to see which government agencies and organizations have requested their data.
- A panel discussion titled “Digital Trust as the Foundation for Digital Transformation in Central Asia,” exploring how to balance digital innovation with the protection of citizens’ rights.
- A live demonstration, “Your Data Against You”—a staged performance illustrating how personal data can be used against individuals, accompanied by practical recommendations. * Panel session: “Personal Data in the Age of AI: Global Standards and Protection Practices” — covering the GDPR and other regulatory models, and their adaptation into national legislation.
- Keynote: “Attack on an Organization” — a demonstration of a large-scale cyberattack scenario in which the data of millions of people is compromised in a matter of minutes.
- Signing of memoranda with regulatory authorities from other countries, and the Data Protection Awards Kyrgyzstan ceremony.
Congratulations to our colleagues on their award! The Data Protection Awards Kyrgyzstan ceremony, which brought together representatives from the public sector, the business community, and experts, served as an opportunity to review the progress made in the country’s legal and technological infrastructure for information security. Following an independent assessment, the National Legal Corporation (NLC), in partnership with the Public Foundation “Civil Initiative on Internet Policy” (CIIP), received the highest level of professional recognition in the category “Leader in Legal Consulting for Personal Data Protection.”
Both the NLC and CIIP are members of the Association and were among its founding organizations. We extend our heartfelt congratulations to our colleagues on this well-deserved honor. This award recognizes their years of dedicated work and contributions to the development of the personal data protection system in Kyrgyzstan, while also confirming that our community is built on a strong foundation of expertise.
Day Two of the Forum: Practical Workshop
The second day of the forum featured a practical workshop, organized as part of the C4CA (Connectivity for Central Asia) project, which focused on hands-on discussions regarding current issues in personal data protection.
The workshop was led by Imane Dahou, an expert in personal data protection and information security. During the session, participants exchanged experiences and deepened their knowledge on how to protect personal data, ensure information security, and apply these approaches in practice. This format complemented the main program: following plenary sessions and discussions, participants had the opportunity to examine specific challenges and continue their professional dialogue.
Why this matters for Kyrgyzstan:
- Personal data protection is evolving into a structured system rather than a mere formality. Five years of the Agency’s operations, the introduction of services for citizens, and various international memoranda demonstrate that the state is shifting from setting requirements to implementing them in practice. For businesses, this means that registration in the data controller registry and the appointment of a designated officer for data processing have become mandatory operational requirements.
- Transparency fosters trust. The ability for individuals to see who has requested their data transforms the relationship between citizens and the state. Digital trust cannot simply be proclaimed; it must be built through concrete mechanisms.
- AI adds complexity. AI models are trained on personal data, while malicious actors exploit this information for personalized attacks and the creation of deepfakes. International standards—such as the GDPR—provide benchmarks that can be adapted to local contexts.
- Data leaks often originate with people. Demonstrations such as “Your Data Against You” and “Attack on an Organization” underscored a point we frequently emphasize during audits and training: most security incidents stem from human error rather than technical hacking.
- Practice outweighs declarations. Workshops where specialists analyze specific data protection techniques help translate legal requirements into functional, day-to-day processes within organizations.
- The region is developing a shared agenda. The involvement of colleagues from Kazakhstan, Tajikistan, and Azerbaijan, along with the C4CA project, demonstrates that data protection issues in Central Asia are being addressed collectively.
Participation in such forums helps the Association better understand the needs of both the government and the business sector. This insight will inform staff training, cybersecurity audits, and support for companies in achieving compliance with personal data legislation.