 Русский
CYBERSECURITY IS OFTEN ASSOCIATED WITH TECHNOLOGY: PROTECTING NETWORKS AND DEVICES, DEPLOYING ANTIVIRUS SOLUTIONS, DETECTING ATTACKS, USING STRONG PASSWORDS AND IMPLEMENTING MULTI-FACTOR AUTHENTICATION. YET EVEN THE MOST ADVANCED TECHNICAL INFRASTRUCTURE CANNOT ELIMINATE ONE OF THE MOST COMPLEX RISK FACTORS — PEOPLE.
Cybercriminals do not only attack systems. They attack people.
Clicking a suspicious link, opening an attachment, reusing a password, postponing software updates, or giving someone access to a device may seem like minor actions. Yet these everyday decisions can create opportunities for attackers to bypass technical safeguards.
This is why human behaviour has become an important part of the cyber attack surface.
Why People Become Targets?
For an attacker, a person can be just as valuable a target as a technical system. People have access to data, money, devices, accounts, corporate resources and identities. An attack can begin with something as ordinary as an email, a link, an attachment, a website or an external device. Additional risks arise when users postpone updates, disable security measures, or rely on unsupported hardware and software.
However, human vulnerability is not simply a matter of insufficient knowledge. People make decisions under time pressure, information overload, stress and constant interruptions. These characteristics of everyday behaviour can be exploited by attackers.
Psychology as a Tool of Attack
Many social engineering attacks rely on completely natural features of human thinking.
Authority Bias:
People tend to trust messages or requests that appear to come from someone they perceive as an authority — a manager, colleague, government institution, bank or other trusted organization.
The Urgency Effect:
Messages that create a sense of urgency reduce the likelihood that a person will stop and verify the information. “Act immediately.” “Your account will be blocked.” “Confirmation is required now.” Such messages are designed to make people act before they have time to critically assess the situation.
Reciprocity
When people receive something useful or helpful, they may naturally feel a need to respond in kind. In a digital environment, this normal social tendency can also be used as a manipulation technique.
Social Proof
People tend to perceive an action as safer when they see others doing the same thing. In the digital environment, this may translate into trusting a message, link, service or request simply because it appears familiar or because others have interacted with it. The attacker therefore does not always need to “break into” a technical system. Sometimes it is enough to create the right situation for a person to take the desired action themselves.
Stress, Information Overload and Multitasking
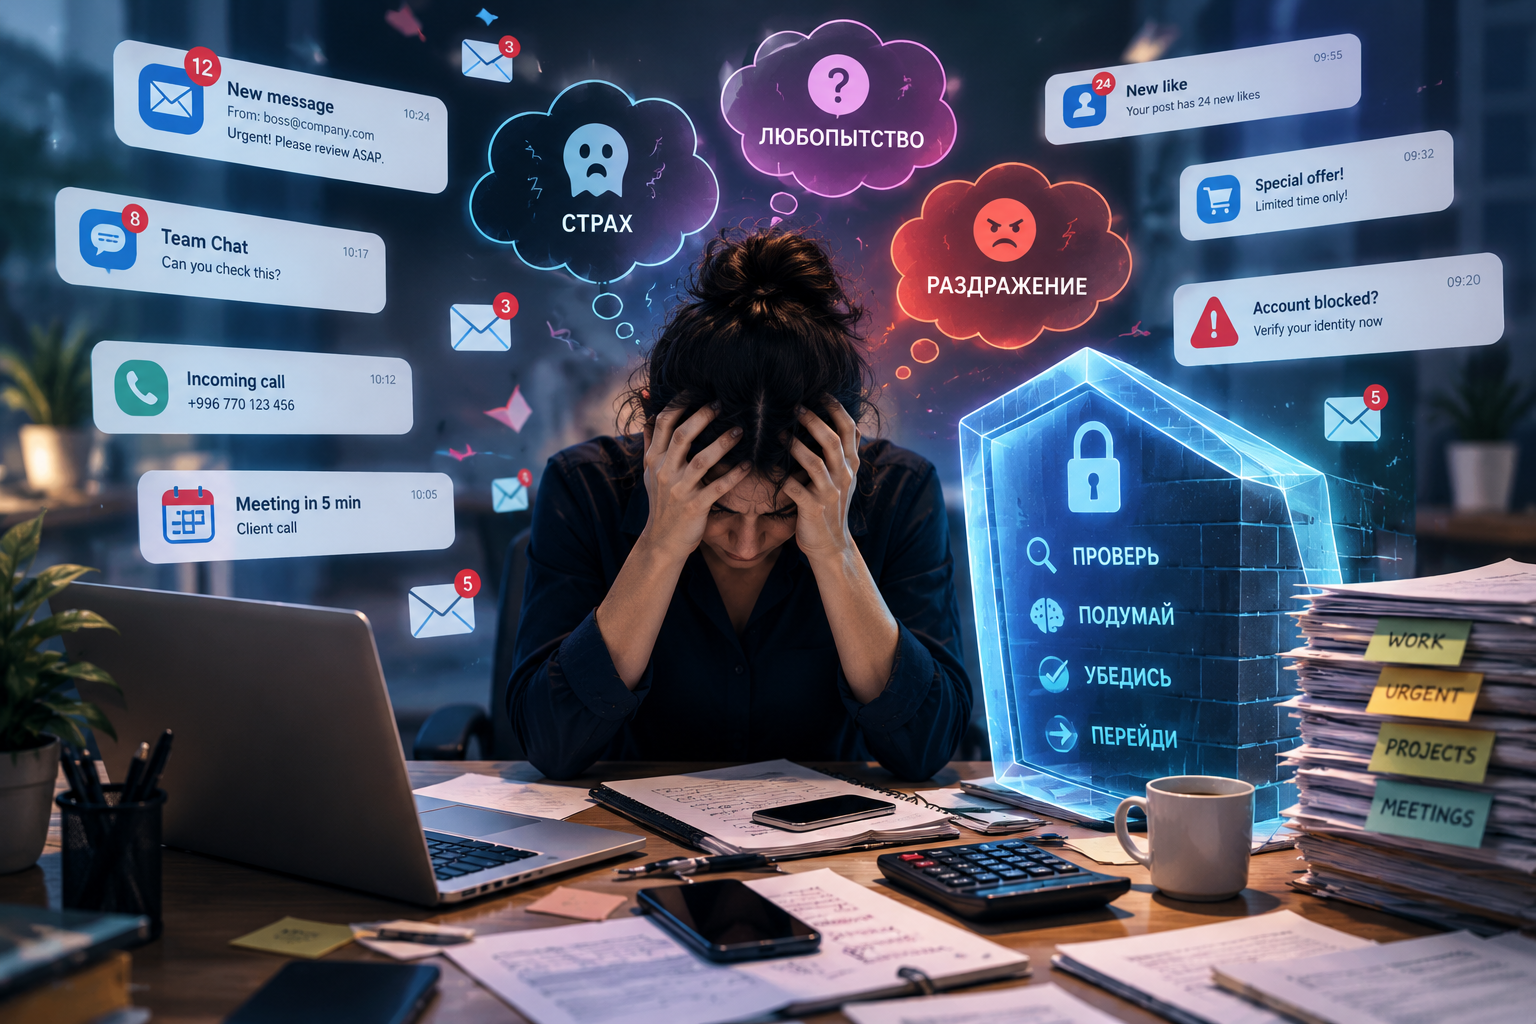
Another important factor is the user’s mental state. Constant rushing, information overload, multitasking and fatigue increase cognitive load. When a person is simultaneously responding to messages, participating in a meeting, working with documents and receiving multiple notifications, their ability to carefully evaluate each individual action decreases.
Under these conditions, security procedures can easily feel like additional obstacles. Emotions can also influence decision-making. Fear, curiosity, irritation, the expectation of a benefit or the desire to solve a problem quickly can all encourage impulsive actions. This means that cybersecurity is not only a matter of knowledge.
It is also a matter of behaviour and daily habits.
From Awareness to Habit
Traditional cybersecurity awareness programmes often focus on education: employees are taught what threats exist and what they should avoid. But knowledge alone may not be enough.
A person may know perfectly well that suspicious links should not be opened and still click one when under pressure, distracted or emotionally engaged. That is why cybersecurity needs to move beyond awareness toward consistent behavioural habits.
Pause Before You Click
Before taking a potentially risky action, take a brief pause.
Notice Your Emotional State
If a message triggers strong fear, pressure, curiosity or an intense sense of urgency, this may be a signal to stop and verify the information.
Single-Task Critical Actions
When performing sensitive actions — logging into an important system, transferring funds, granting access or handling confidential information — reducing multitasking can help maintain attention.
Breathe and Check
A short pause before acting creates an opportunity to check the sender, address, link, context and actual necessity of the requested action.
Name the Manipulation
Recognising the psychological technique being used — authority, urgency, social pressure or emotional manipulation — can make it easier to step back from the situation and evaluate it objectively.
Build Daily Micro-Habits
Cybersecurity becomes more resilient when secure behaviour becomes part of everyday routine rather than a set of rules remembered only during an annual training session.
The Human Factor Is an Organisational Issue.
It is important not to turn discussions about the human factor into a process of blaming employees. When an organisation treats people simply as the “weakest link”, it can overlook a more important question:
Why is secure behaviour difficult to maintain in the existing working environment?
The number of notifications, complexity of procedures, excessive multitasking, poorly designed systems and constant pressure to act quickly can themselves create additional risks. Organisations therefore need not only to educate employees but also to create an environment in which the secure choice is the simple and understandable choice.
This can include:
- regular cybersecurity awareness and practical scenario-based training;
- clear procedures for verifying suspicious messages and requests;
- secure processes for granting access;
- timely software and security updates;
- limiting unnecessary access privileges;
- simple mechanisms for reporting suspicious activity or mistakes;
- creating a culture where reporting an error is not automatically seen as grounds for punishment, but as an important part of organisational defence.